29°C
Claro Dominicana Reports Unauthorized Exposure of Customer Data
Claro Dominicana has notified individual mobile customers of an unauthorized exposure of personal data, while the Dominican telecommunications regulator, INDOTEL, is following the case with national cybersecurity authorities.


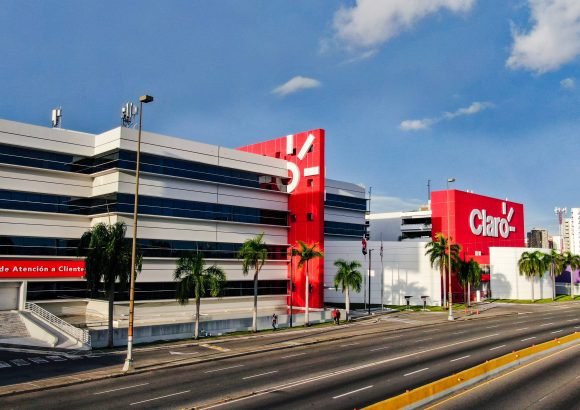
Claro Dominicana has reported an unauthorized exposure of personal information involving a group of individual mobile customers, prompting the company to activate its security protocols and begin an investigation into the scope of the incident.
The telecommunications company said the information identified so far includes mobile phone numbers, national identification numbers and the type of service contracted. Claro said these data, on their own, do not provide access to customer accounts, allow transactions to be carried out or reveal the content of communications.
INDOTEL Is Following the Investigation
The incident has also drawn the attention of the Dominican Institute of Telecommunications (INDOTEL), the country’s telecommunications regulator. The agency said it is following the case and coordinating with the National Cybersecurity Center (CNCS) and other competent authorities as investigations continue.
INDOTEL said the information about the exposed data was reported by Claro and is being contrasted as part of the verification process. The authorities are working to establish the scope of the incident and identify those responsible, according to information released after Claro’s notification. :contentReference[oaicite:0]{index=0}
As of the latest public information, Claro has not disclosed how many customers were affected. The company has described the incident as involving a group of individual mobile customers, while the investigation remains underway.
What Information Was Exposed
The categories identified by Claro are limited, according to the company’s current account of the incident, to mobile telephone numbers, identification numbers and information about the type of contracted service. The company has specifically said that these elements do not, by themselves, provide access to customer accounts, enable transactions or expose the content of communications.
That distinction is relevant for customers because the exposure of personal information does not necessarily mean that account credentials or communications have also been compromised. However, exposed contact and identification information can still be useful to people attempting to impersonate a company or customer in subsequent social-engineering or phishing attempts.
Customers Are Being Advised to Strengthen Security
Claro Dominicana has directed customers to its security information resources, where it recommends measures such as using strong passwords, avoiding the disclosure of passwords or verification codes in response to unsolicited calls or messages, enabling multifactor authentication where available and avoiding suspicious links. :contentReference[oaicite:2]{index=2}
The company’s security guidance also warns users to be cautious about sharing personal information through text messages, applications and social networks. These precautions are particularly relevant following an incident involving customer identification and contact information, because criminals can use legitimate-looking personal details to make fraudulent communications appear more credible.
Claro’s customer-support portal provides assistance for service-related requests and complaints, while its online services allow customers to manage and review aspects of their accounts. :contentReference[oaicite:3]{index=3}
Investigation Remains Ongoing
Claro said it activated its specialized security team after detecting the exposure and began verifying the circumstances and scope of the incident. INDOTEL’s involvement adds a regulatory layer to those efforts, with the agency coordinating with the CNCS and other authorities.
For now, the publicly identified information concerns customer phone numbers, identification numbers and contracted service types. Further details about the number of affected customers, the circumstances that led to the exposure and any additional information that may have been involved have not been publicly established in the latest reports.