28°C
Gambling Goblin Hijacks Trusted Government Websites for Betting
A Chinese-speaking cybercrime group known as Gambling Goblin has been compromising Linux web servers operated by Brazilian government and educational institutions, turning trusted domains into covert gateways for gambling promotions and fake app downloads. The campaign, tracked since mid-2025, is designed to exploit the search authority and public trust associated with institutional websites.


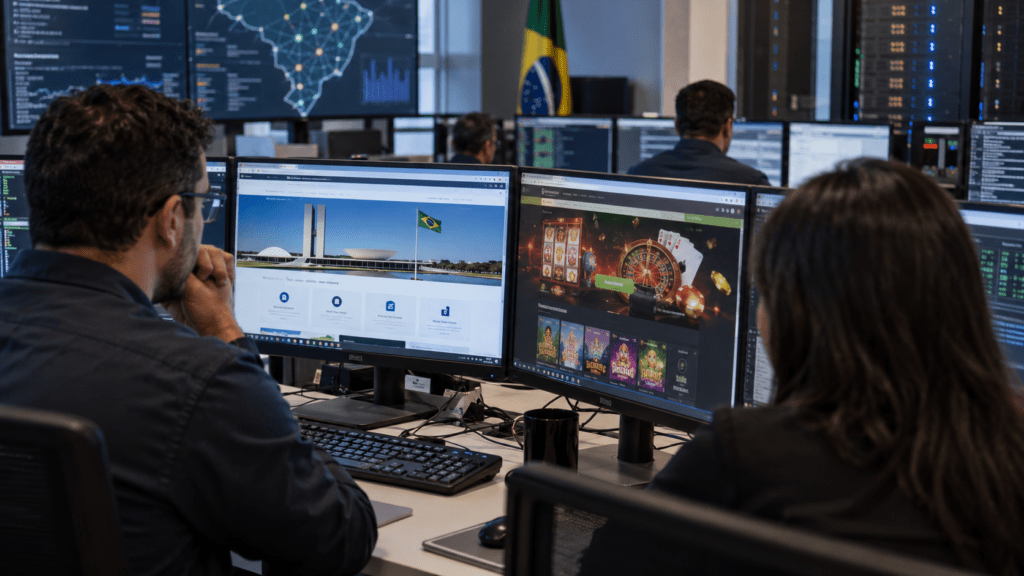
Gambling Goblin is using compromised government and educational infrastructure in Brazil to redirect visitors toward online gambling and deceptive download pages while leaving the legitimate institutional URL visible in the browser. The technique allows attackers to abuse the reputation of trusted websites without carrying out a conventional homepage defacement.
Check Point Research, which identified and named the group, said the campaign has been active since at least mid-2025. The operation primarily affects Brazilian public-sector infrastructure, but the broader network has been prepared for Spanish-, English- and Vietnamese-speaking audiences, indicating that the model is designed to operate beyond a single country.
A Government URL Can Become a Hidden Gateway
The attackers’ approach relies on malicious modules installed in Apache web servers running on Linux. Rather than simply replacing the visible content of a website, the modules can act as reverse proxies, selectively sending visitors to infrastructure controlled by the attackers.
The browser can continue displaying the legitimate government address even while the content being delivered originates from an attacker-controlled system. That makes the scheme particularly deceptive: a visitor may believe that a page is trustworthy simply because the official domain remains visible.
Researchers also found that the malicious modules can interfere with security headers, including Content Security Policy protections, and apply filters based on factors such as location or user-agent. This selective behavior can make the malicious content harder for automated security systems to observe.
Attackers Are Exploiting Search Engine Trust
The campaign goes beyond deceiving individual visitors. Gambling Goblin appears to be using compromised institutional domains as part of a large-scale SEO fraud operation, taking advantage of the high reputation that government and educational websites can accumulate in search engines.
Check Point found compromised Brazilian government domains being used to support pages that impersonated well-known digital storefronts, including Google Play, Microsoft Store and Amazon. Behind the familiar designs, the pages promoted online gambling and sports betting.
By linking compromised high-reputation domains with fraudulent content, the operators can attempt to increase the visibility of gambling-related pages in search results. Check Point described the operation as an industrialized abuse of institutional trust rather than a conventional website defacement.
The Linux Infrastructure Behind the Campaign
The malicious Apache modules are only one component of a broader Linux toolkit identified by researchers. The operation includes a downloader, backdoors, credential-stealing capabilities and reconnaissance tools used to map internet-facing systems.
Researchers identified components including DownPro, AlphaAgent and oRAT, along with a credential-stealing tool derived from 3snake. The toolkit is heavily obfuscated, making analysis and detection more difficult.
The use of malicious modules embedded directly into the web server also creates a detection challenge. Conventional monitoring focused on website files may fail to identify suspicious activity if the attacker instead modifies the server’s module configuration or loads malicious code within the legitimate Apache process.
Why the Campaign Matters Beyond Brazil
Brazil is the main focus identified in the current investigation, including federal, state and municipal institutions as well as educational organizations. However, the presence of localized infrastructure in Spanish and English means that the underlying operation has a broader potential audience.
There is no indication in the research reviewed for this report that Dominican government websites have been compromised by Gambling Goblin. The relevance for the Dominican Republic lies instead in the technique itself: public institutions, universities and other organizations operating Linux-based web infrastructure could face similar forms of domain abuse if attackers gain sufficient access to their servers.
The incident also illustrates why the compromise of an institutional website can have consequences beyond the organization that operates it. Once a trusted domain is used to distribute fraudulent content, visitors can be deceived, search results can be manipulated and confidence in legitimate online government services can be damaged.
A Potential Path to More Dangerous Attacks
For now, the observed operation is heavily focused on gambling promotion, phishing and search manipulation. But the infrastructure creates a more serious possibility because the same trusted pages are already being used to imitate legitimate application stores.
Check Point warned that a change in the attackers’ configuration could allow the infrastructure to be used for direct malware distribution. That makes the campaign significant even for organizations that are not themselves involved in online gambling: the compromised domain becomes an asset that can potentially be repurposed for other forms of cybercrime.
For public-sector security teams, the case underscores the need to monitor not only website content but also Apache modules, server configurations, security headers and unexpected outbound connections. The attack demonstrates that protecting an institutional domain increasingly means protecting the infrastructure and reputation behind the domain, not simply keeping the homepage online.